Strengthening Trust Wallet's download processes with user focus Safe Trust Wallet Download Tips
admin 2026年9月27日 14:14:47 trustwallet安卓版下载 1
Strengthening Trust Wallet's download processes with user focus Safe Trust Wallet Download Tips
Trust Wallet has become a default choice for millions managing crypto assets,yet the moment you start searching for the download, the experience often gets noisy. Fake APK files, phishing links embedded in "support" emails, and third-party mirrors clutter the results. What users really need is a download flow that puts their safety at the center—clear, verified, and free from guesswork. The steps below cut through the clutter and focus on what actually protects you.
The only safe sources are the official Trust Wallet website and the two major app stores: Apple App Store for iOS and Google Play for Android. On the website, verify the URL reads "trustwallet.com" exactly, with the padlock icon present. In the app stores, the developer name should display as "Tether Technologies" or "Trust Wallet"—tap it and confirm it links back to the official domain. Any other developer name, no matter how similar it looks, is a red flag worth walking away from.
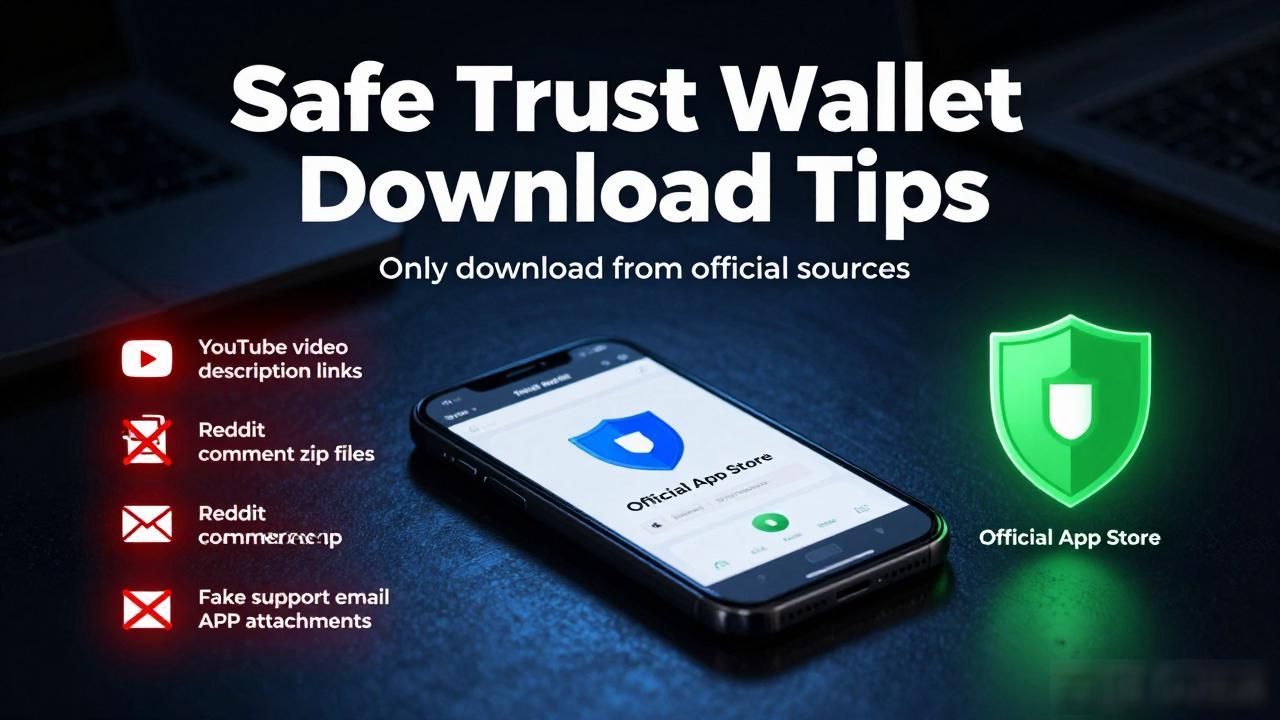
Where downloads go wrong is usually off-platform. A YouTube video pinning a link in the description,a Reddit comment with a .zip fileStrengthening Trust Wallet's download processes with user focus Safe Trust Wallet Download Tips, or a "Trust Wallet support" email with an attached APK—each one is a vector for a trojan that steals your seed phrase the moment you open it. Never install a .apk from a browser or email attachment. Android's "install unknown apps" prompt exists,but using it for a crypto wallet is an invitation to lose everything.
After the app opens for the first timeStrengthening Trust Wallet's download processes with user focus, read the permission list before granting access. Trust Wallet should request storage for seed-phrase backup and notifications for price alerts. It should not demand SMS, contacts, or location access. If a permission looks out of place, deny it and recheck your download source. The wallet itself should display a verified developer signature in the Android system settings under "Security" or the iOS "App Management" screen.
The broader shift is simple: every design decision in the download pipeline should answer one question—does this reduce the user's risk or add to it? Clearer store listings with tamper-evident checkmarks, one-tap verification of the developer identity, and a post-install security checklist would close the gaps that currently push users toward sketchy alternatives. The wallet is only as strong as the path that delivers it to a phone.